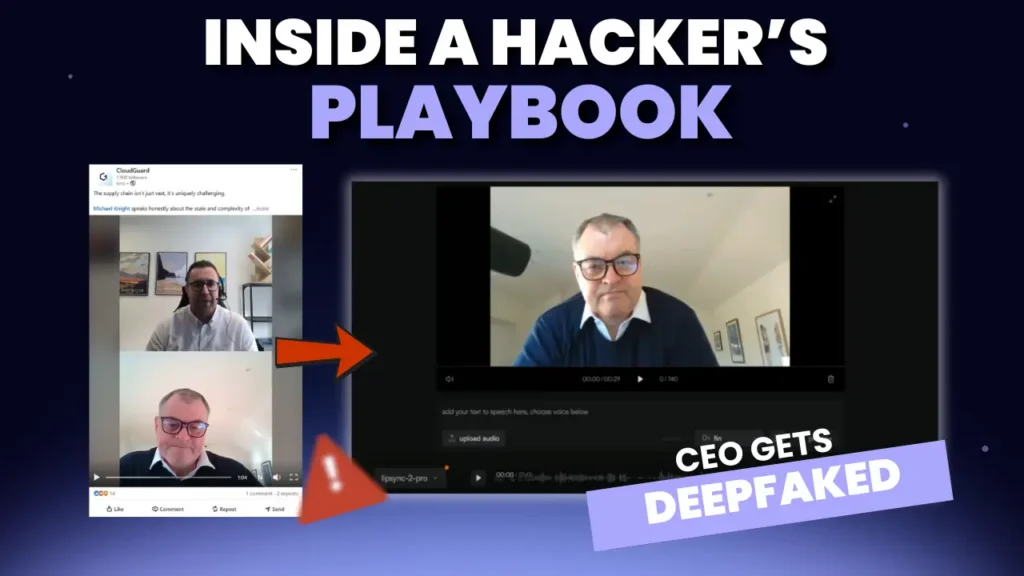
Cyber warfare is shaping the way individuals and organisations interact, communicate, and protect their assets. At the heart of this escalating conflict are two opposing forces – Automated Cyber Attacks and Automated Cyber Security. Let’s dive into the world of automated warfare, exploring the capabilities, risks, and defences employed by each side in this relentless cyber showdown.
In the red corner: Automated cyber attacks
An army of malicious bots and sophisticated algorithms are continuously seeking vulnerabilities in networks, applications, and systems. These are the foot soldiers of Automated Cyber Attacks. Like clockwork, they identify weaknesses, probe for backdoors, and exploit any loopholes they can find.
One of the main advantages of automated attacks is their speed and scale. Unlike human hackers, who may take days or even weeks to devise and execute an attack, automated tools can launch multiple strikes simultaneously, overwhelming targets in a matter of seconds. Even scarier, these attacks can happen around the clock, never resting or showing any sign of fatigue.
Automated cyber attacks come in various forms, including Distributed Denial of Service (DDoS) attacks, ransomware campaigns, and phishing campaigns. They are driven by the objective of stealing sensitive information, extorting money, or causing widespread disruption for political or ideological motives.
This report from Recorded Future highlights to top 10 most automated cyber attacks.
In the blue corner: Automated cyber security
Facing the relentless barrage of automated attacks, cybersecurity has evolved to fight fire with fire. Automated Cyber Security is an amalgamation of technologies, machine learning algorithms, and human expertise.
Automated Cyber Security uses intelligent tools that continuously monitor network activity, seeking out suspicious patterns, and identifying potential threats in real-time. This proactive approach allows organisations to stay one step ahead of potential attackers, blocking them before any damage occurs.
Machine learning plays a pivotal role in improving cyber defences. By analysing vast amounts of data, these algorithms can detect anomalous behaviour, predict emerging threats, and fine-tune security measures. As the battle rages on, the defence mechanisms learn from each encounter, becoming smarter, more efficient, and better equipped to face future threats.
Collaboration is the key
The world of cyber warfare is a complex ecosystem. While automated cyber security systems have made significant strides in protecting businesses, a collaborative approach is crucial for effectively countering automated attacks.
Security analysts still play a critical role in interpreting data, identifying false positives, and devising strategic responses to sophisticated attacks. The seamless integration of human expertise with automated cyber security systems creates a strong defence against even the most advanced threats.
The risks of automation
As with any technological advancement, the reliance on automation in cybersecurity is not without its risks. False positives, for instance, can lead to unnecessary disruptions and create an atmosphere of uncertainty within organisations. Automated systems are only as effective as the rules they are given and data they are fed. Attackers can exploit outdated information and blind spots to find a way into your systems.
Another potential concern lies in the weaponisation of AI. Attackers may utilise AI-powered tools to devise even more targeted and potent attacks. As AI continues to advance, it becomes essential for the all businesses to stay ahead of these malicious applications of AI technology.
Striking the balance
Striking the right balance between automation and human intervention is important. While automation improves the speed and efficiency of cyber security, human ingenuity and adaptability are always going to be needed.
One solution that perfectly balances this is MXDR or Managed Extended Detection and Response. This AI-powered solution deploys automated threat detection and automated incident response processes to give security analysts more time to investigate and remediate more serious incidents.
You should also invest in regular training and education for your cybersecurity teams. This helps keep them up-to-date with the latest threats and trends. In doing so, you help your security teams to make informed decisions and outsmart their automated adversaries.
The future of automated cyber security
Automated Cyber Attacks and Automated Cyber Security will continue their perpetual battle. As technology advances, so will the sophistication of attacks and defences. By embracing the power of automation, and recognising the ongoing importance of human expertise, you can tilt the odds in your favour . Just as automated attackers never rest, we must remain vigilant and adaptive, ensuring the bytes of tomorrow are safe from the threats of today.